Built with Claude
 ChatGPT
 Cursor
 Lovable
 GitHub Copilot
 Gemini
 v0
 Replit
 Windsurfvibe
coding
Expert review
before you ship
Check services built with AI tools like Claude, Cursor, and Lovable
Upload your code and see a transparent quote right away.
Drag and drop your code ZIP, or click to select
Up to 100MB · Zip your project root and upload it
Cestdi is
with you
From launch to operations, we stay by your side for the service you built with vibe coding.
$110
Avg. quote
2 days
Avg. review time
100+
Projects delivered
3,257
Avg. LOC
We don't have
a developer
Former-CTO working experts with 10+ years each in Web, Backend, Android, and iOS review the code you built with vibe coding in detail.
The review report also covers what you'll need for operations — env variables, cloud deployment, and more.!
Outsourcing quotes vary so wildly,
how do I even choose?
A transparent pricing system means fair prices for extra work. You can outsource just a single feature, like payments or social login.
We also handle the hard parts for you — building the admin dashboard and PG payment approval.!
Keep vibe coding,
we'll keep checking it
Focus on validating your market. We'll keep verifying it's built right, every time you deploy.
We'll keep watching at a reasonable cost, so your launches, edits, and deploys stay just as fast.!
Am I doing
vibe coding right?
Going it alone without dev knowledge has its limits. Prompt and rule setup changes your code quality — we'll help you get it right.
For our clients, we provide per-AI guides built on our review know-how.!
Claude
CLAUDE.md
Cursor
.cursor/rules
Codex
AGENTS.md
5 minutes is all it takes
Just archive your code and send it over
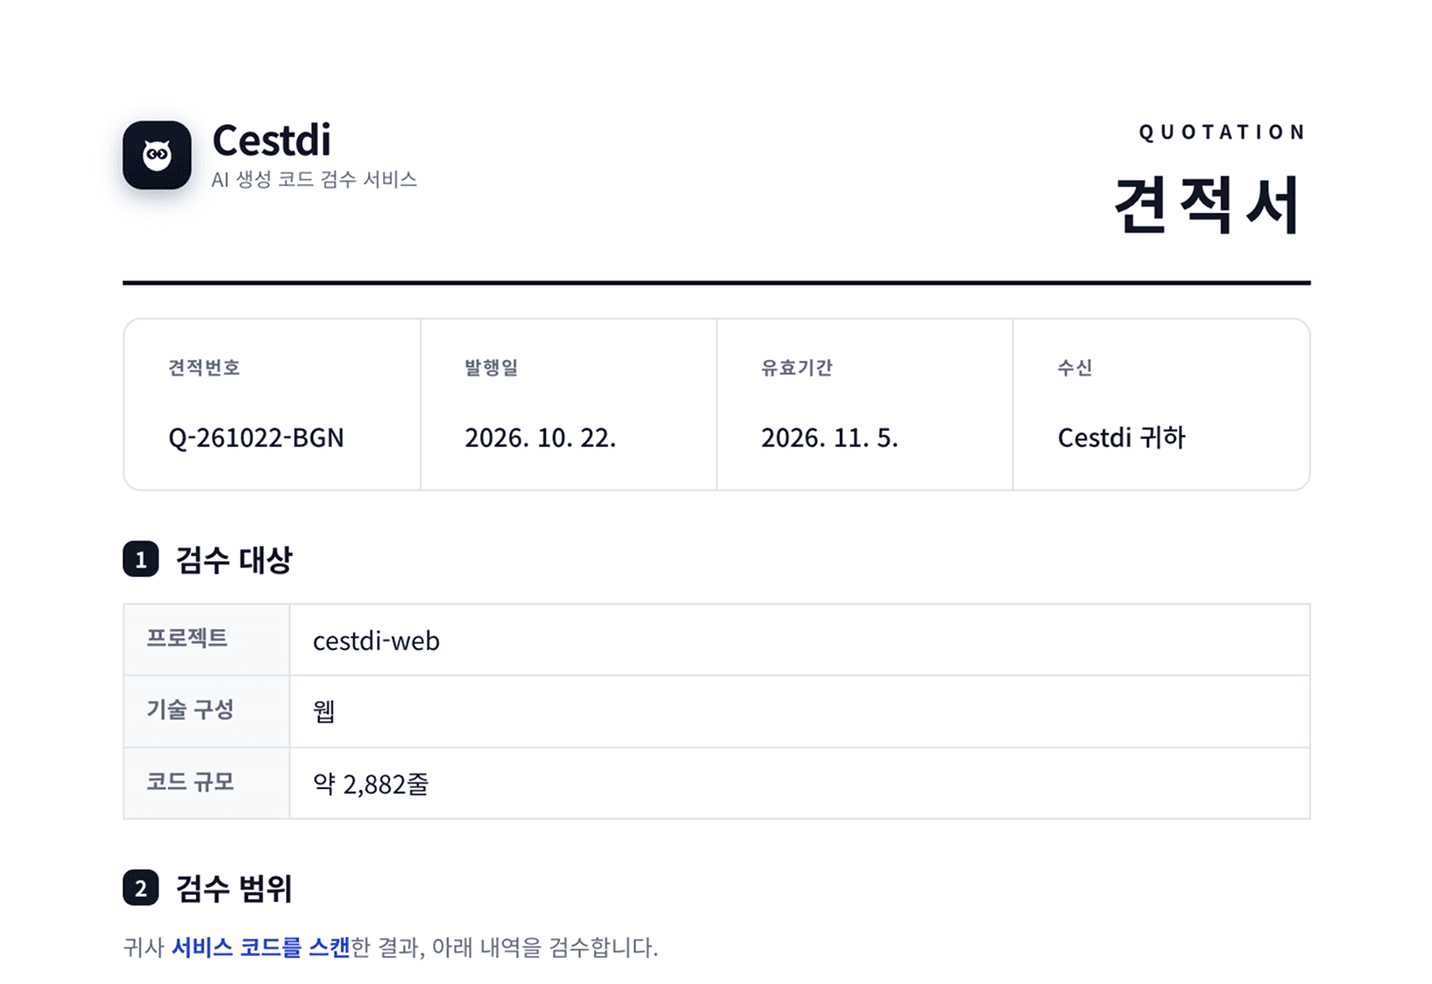
Based on the audit report,
we solve the problems with you
Scope of audit
Inspection scope
Payment security
3 items- HighAmount tampering protection
- MedStock · balance · refund consistency

Security
Core vulnerabilities — payment tampering, secret exposure, access bypass (IDOR), and more
Login · Access
9 itemsLogin, session and access-control safety
Data · Secrets
9 itemsSecrets, DB and storage access control
AI features
3 items- MedAI abuse · cost theft · prompt tampering
- MedAI response handling stability

Cost
Detects runaway-cost risks from unguarded external calls and unlimited retries
Web · Ops
12 itemsCommon web vulns · operational security
Reliability
7 items- MedBrute-force · abuse defense
- LowMissing error handling

Reliability
Failure points under traffic spikes, slow queries (N+1), missing error handling
Findings · Fixes
api/link-preview/route.ts:104
FixAdd a DNS check before fetch to block private/reserved IPs. Fix before deploy.

Findings report
We diagnose and propose fixes — resolve via prompt edits or per-item outsourcing
no next.config
FixAdd CSP · HSTS · X-Frame · nosniff headers.
create-checkout-session.ts:15
FixRemove console.log; stop returning err.message to the client.
Add-on quotes

Per-item outsourcing
Custom outsourcing — from tricky env-var setup to PG (payment) provider review

Regular maintenance
Periodic audits of your vibe-coded product for safer operation
Solve issues together with Cestdi and ship with confidence.
Just upload your code — our experts take it from there

Upload code
Zip your project and upload it right here on this page.

Instant quote
Instantly see a transparent quote based on code size, check items, and more.

Expert review
A hands-on expert (ex-CTO) audits your code item by item.

Solve problems
Vulnerability diagnosis and fixes — plus per-item development for a fast launch.
Frequently asked questions
The questions we get most about scope, turnaround, pricing, and how your code is handled.
We review your uploaded code against 45 security, reliability, and cost checks. The focus is on critical issues such as payment amount tampering, exposed secrets, authorization bypass (IDOR), RLS configuration, and unauthenticated calls to paid APIs. The review is limited to code, UI, and process; it does not include legal advice or similar services.
It varies with codebase size and the number of checks, but typically takes 2 to 7 days. We start as soon as your payment is confirmed and keep you updated on the service screen and by email.
Source code is accessed read-only. After the review, unless you continue with a maintenance contract or similar engagement, it is discarded after a set period.
SSR frameworks such as Next.js and Nuxt, servers built with FastAPI, Express, or NestJS, Supabase and Firebase, and mobile apps built with Expo, React Native, or Flutter. Whether you used Claude, Cursor, Lovable, Bolt, or v0, just zip the project and upload it.
The report explains the cause and fix for each issue, so you can apply the fixes yourself. For harder pieces such as payment integration, social login, or an admin page, you can outsource individual features to us, and we also help prepare for payment gateway certification. Outsourcing is quoted separately.
After reviewing the quote, you make a bank transfer to the account shown; once the Cestdi team confirms the deposit, the review begins. Tax invoices are available on request. See the Terms of Service for details.
You receive a PDF report listing the findings in order of severity. Each finding includes its impact, cause, and fix, along with operational notes such as environment variable setup and cloud deployment. It is written so that non-engineers can read it.
No developer on your team?
Work with an external CTO
Upload your code and get a quote instantly.